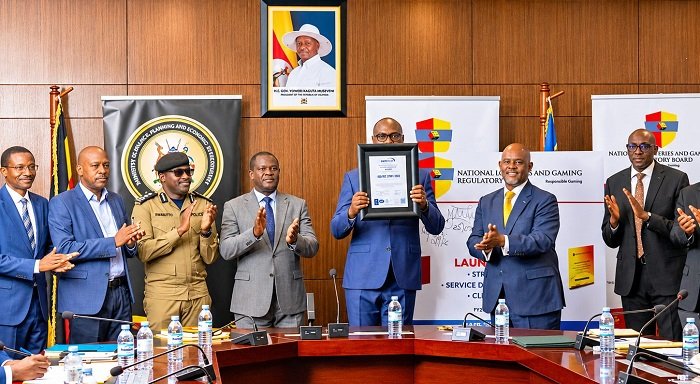
The National Lotteries and Gaming Regulatory Board (NLGRB) has achieved international information cybersecurity certification, reinforcing its commitment to protecting sensitive data, improving regulatory oversight and promoting safer digital gambling operations.
Uganda’s National Lotteries and Gaming Regulatory Board (NLGRB) has received ISO/IEC 27001:2022 certification, marking a milestone in its efforts to strengthen cybersecurity and protect sensitive information. The certification recognizes the Board’s information security management system, which sets out how it identifies, assesses and manages risks across its operations.
It applies to the NLGRB’s Kampala head office, including its personnel, supporting systems and information assets. Chief Executive Officer Denis Mudene Ngabirano described the certification as an important institutional achievement. He said protecting information is a fundamental responsibility for a regulator that handles confidential records from gambling operators and members of the public.
The NLGRB oversees casinos, sports betting and lottery operations in Uganda. As the country’s gambling sector becomes more digital, the regulator’s work increasingly depends on secure systems and reliable information management. ISO/IEC 27001 is an international standard for establishing, implementing and maintaining an Information Security Management System, or ISMS. It helps organizations identify potential threats, assess vulnerabilities and put appropriate controls in place.
The standard is built around three principles: confidentiality, integrity and availability. In practice, this means keeping information accessible to authorized users, protecting it from unauthorized changes and ensuring it is available when needed. For the NLGRB, certification involved reviewing how information is handled across the organization and setting procedures for managing security risks.
The approach goes beyond technical measures such as firewalls, endpoint protection and access restrictions. It also includes organizational policies, staff responsibilities, risk assessment and ongoing review. Ngabirano said the certification should be seen as a strategic investment in governance, not simply a compliance exercise. The Board has also acknowledged that technology now plays a central role in its daily work, making information security essential to the delivery of regulatory services.
The regulator regularly receives sensitive material as part of its supervisory work. This includes licensing documents, compliance records and other information submitted by gambling businesses. It also processes information involving members of the public. Ngabirano said ISO/IEC 27001 certification demonstrates the Board’s commitment to protecting those records through internationally recognized security practices. Maintaining public confidence, he said, depends in part on the regulator’s ability to handle confidential information responsibly.
Information security is not limited to the technology division, according to Isaac Koshaho, a senior licensing officer at the NLGRB. Licensing work involves substantial amounts of confidential information from both regulated businesses and members of the public, making security relevant to employees across the organization. The ISO/IEC 27001 framework sets out responsibilities and procedures intended to help staff understand their role in protecting information.
By incorporating those expectations into routine work, the Board aims to reduce vulnerabilities and strengthen accountability across its operations. The expansion of online betting and digital gaming has increased both the volume and sensitivity of information handled by gambling regulators. As more gambling activity moves online, regulators need to monitor operators while also safeguarding the systems and data used for supervision.
For the NLGRB, this means considering how information is collected, stored, accessed and shared throughout its regulatory processes, not only how its internal computer networks are protected. Digital transactions, customer records and regulatory reporting are becoming more important to the industry. The Board’s certification provides a framework for managing the related security risks as it continues to modernize its operations.
The NLGRB worked with Sentinel Africa Consulting Uganda during its certification process. Stella Makona Simiyu, the company’s co-founder and managing director, said the standard offers a coordinated way to manage cybersecurity risks rather than addressing vulnerabilities through separate technical measures. The framework brings together security governance, risk management, operational controls and continuous improvement.
It also involves independent assessment and ongoing oversight to help organizations maintain the required standards. The Board said the collaboration helped align its information security practices with internationally recognized requirements. The certification is also expected to support the NLGRB’s oversight of licensed gambling operators. Stronger internal information security can help the Board protect the data it relies on to monitor compliance and carry out its supervisory duties.
Compliance official Gershom Lukwago said information security is connected to player protection and the development of secure, transparent gaming environments. As operators expand their digital services, the regulator may also encourage stronger cybersecurity practices across the industry. Protected and accurate information is important to effective supervision.
A regulator needs reliable records to assess whether operators meet their obligations, while safeguards help maintain the confidentiality of information received in the course of that work. The NLGRB described itself as one of Uganda’s early government institutions to obtain an internationally recognized information security certification. Its experience may offer a reference point for other public agencies and private organizations seeking to formalise their approach to cybersecurity.
Koshaho said aligning organizational procedures, technology systems and information management with international standards can support stronger institutional performance. Sentinel Africa Consulting also highlighted the potential value of structured information security management beyond the gambling sector. Following the certification, Ngabirano encouraged leaders in both the public and private sectors to treat information security as a strategic priority.
He stressed that safeguarding sensitive data requires sustained commitment, rather than a one-time technical project. The Board acknowledged the contributions of its employees, management and board members, as well as the Ministry of Finance and Sentinel Africa Consulting Uganda, to the certification process. Certi-Trust issued the NLGRB’s ISO/IEC 27001:2022 certification for the period from June 9, 2026, to June 8, 2029. The certification is subject to annual surveillance audits.
The achievement gives the Board a formal framework for managing information security risks through governance, risk assessment and continuous improvement. As gambling services in Uganda become increasingly digital, the regulator says the certification will support its efforts to protect confidential information and maintain secure regulatory operations.